security solutions
Fortinet Secure Networking
Digital acceleration has led to a rapid expansion of attack surfaces and creation of new network edges, including LAN, WAN, 5G, remote workers, and clouds. Fortinet’s Secure Networking approach is the industry’s only converged networking and security platform. This convergence enables AI-powered defense of today’s highly dynamic environments while enabling better productivity and user experience.
security solutions
Fortinet Secure Networking
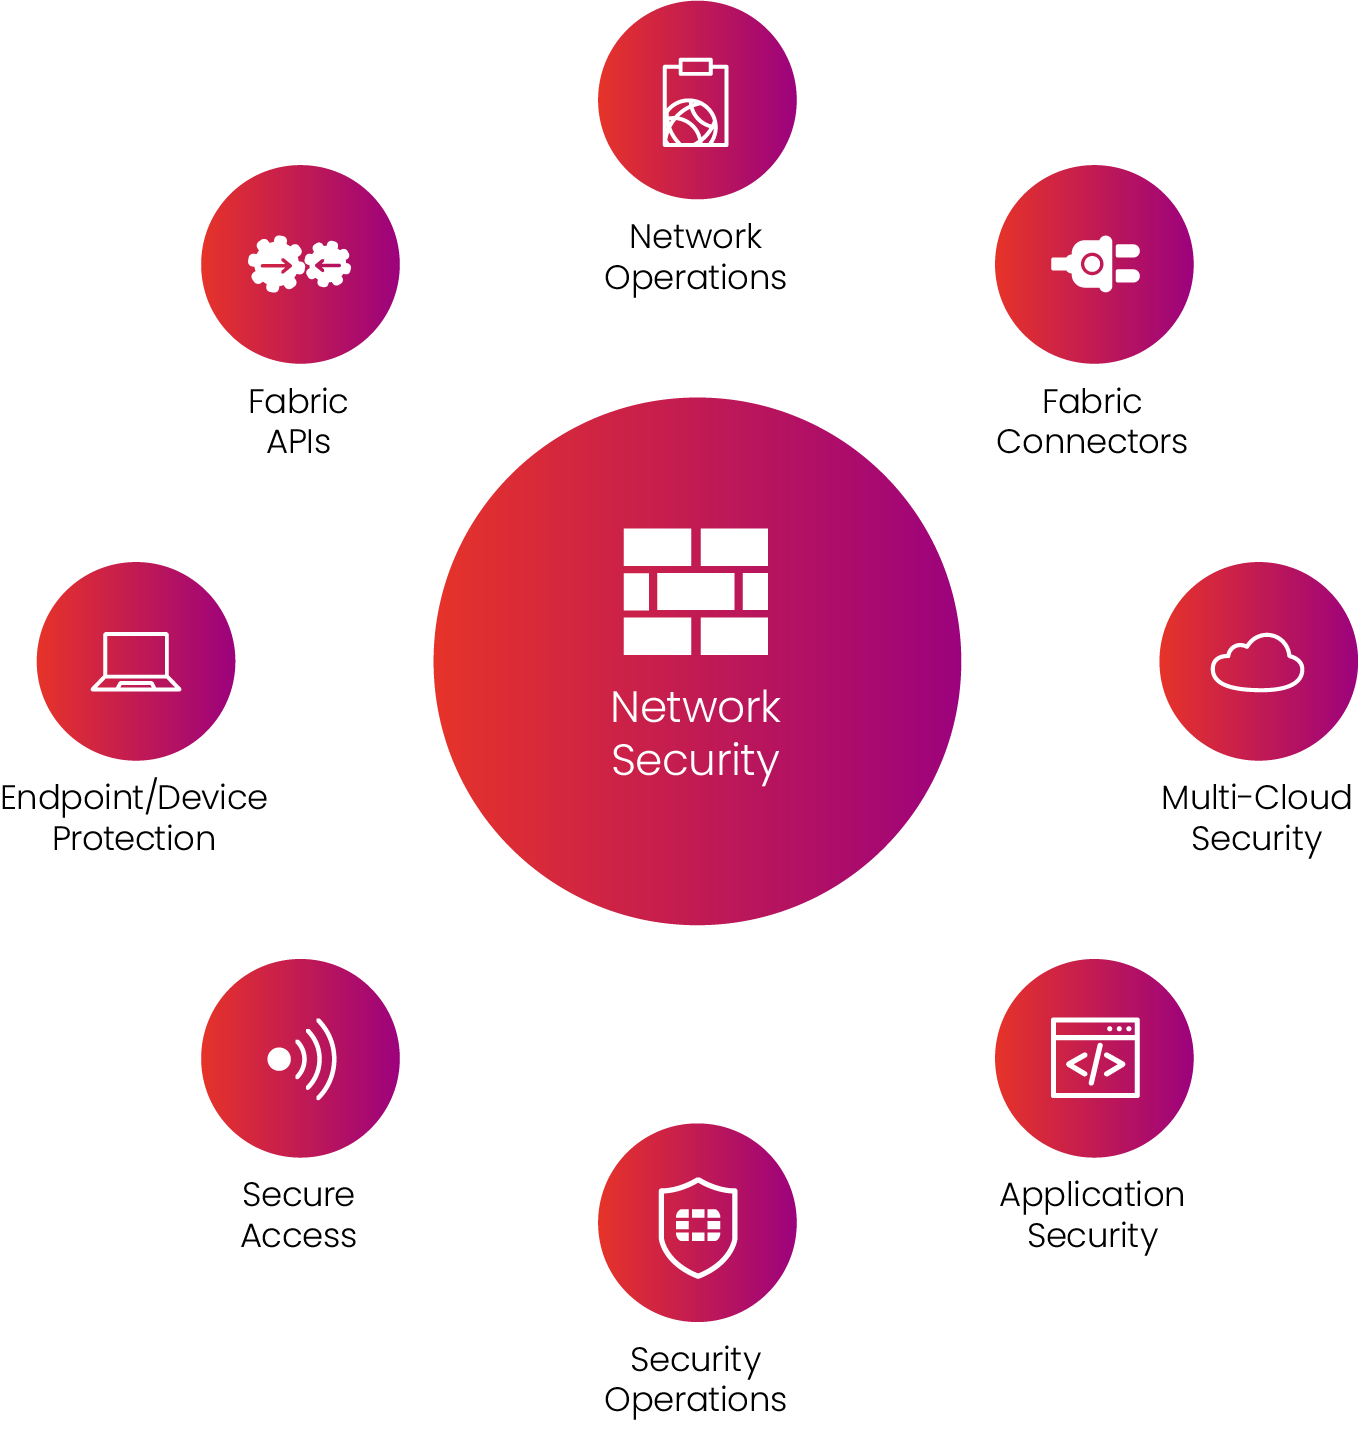
Digital acceleration has led to a rapid expansion of attack surfaces and creation of new network edges, including LAN, WAN, 5G, remote workers, and clouds. Fortinet’s Secure Networking approach is the industry’s only converged networking and security platform. This convergence enables AI-powered defense of today’s highly dynamic environments while enabling better productivity and user experience.
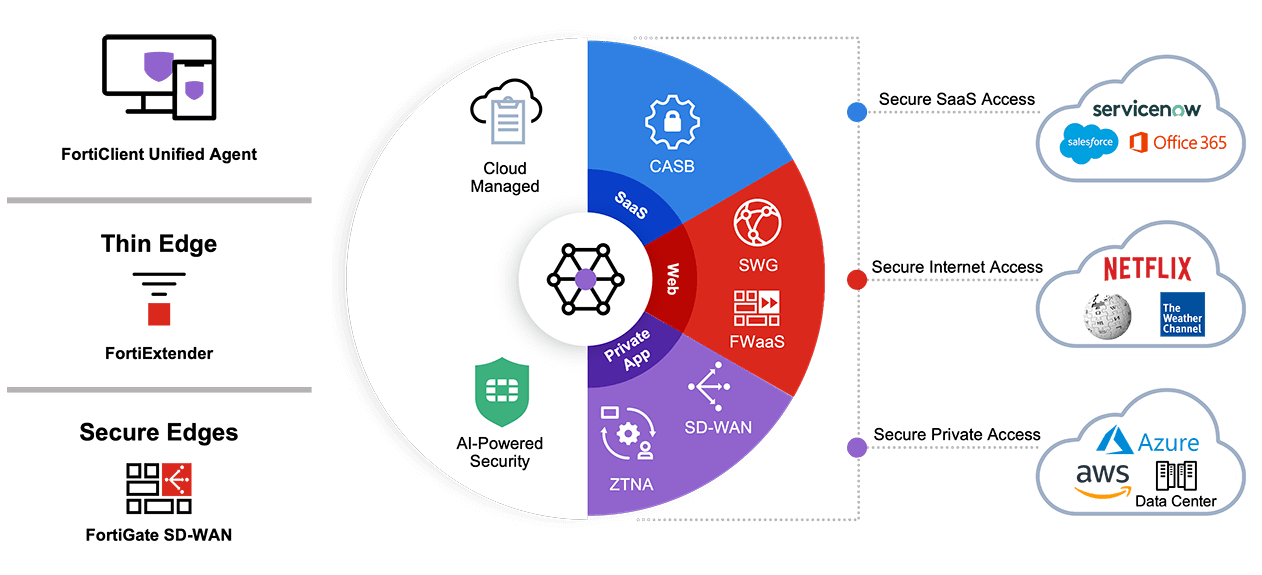
The FortiGate NGFW is the core component of Secure Networking. FortiGate is powered by the FortiOS operating system and purpose-built security processors (SPUs). These innovations enable the most complete convergence of networking and security by eliminating the need for point products. Our unified offering of SD-WAN, NGFW, SWG, ZTNA enforcement, LAN and WLAN, and wireless WAN 5G/LTE are available to deploy on any network edge.
FortiGuard Labs monitors the worldwide attack surface and employs AI to mine data for new threats, ensuring you are prepared for what’s coming. Our threat experts work around the clock to develop, enhance, and enrich FortiGuard AI-Powered Security Services with the very latest threat intelligence. These services are integral to providing Fortinet’s Secure Networking solution with market-leading security capabilities. These solutions and services work together to provide the best protection for your applications, content, web traffic, devices, and users located anywhere.
-
Increase Security with Access Solutions
As users continue to work from anywhere and IoT devices flood networks and operational environments, continuous verification of all users and devices as they access corporate applications and data is needed. To protect networks and applications, network administrators must implement a zero-trust access approach and provide least access privileges. Implementing zero-trust access includes requiring strong authentication capabilities, powerful network access control tools, and pervasive application access policies.
-
Remote Access and Application Access
Applying the zero-trust security model to application access makes it possible for organizations to move away from the use of a traditional virtual private network (VPN) tunnel that provides unrestricted access to the network. Zero-trust network access (ZTNA) solutions grant access on a per-session basis to individual applications only after devices and users are verified. This ZTNA policy is also applied when users are on the network, which provides the same zero-trust model no matter the user’s location.
-
Endpoint Security: Protect, Detect, and Respond
Fortinet delivers advanced endpoint protection to stop threats and ransomware from infecting your devices. Our EDR solution also hunts threats that may be lurking in your system. Near real-time, automated threat intelligence from FortiGuard Labs ensures users are protected—without manual oversight —from known threats and unseen variants. Integrated network and endpoint security give administrators visibility and control from a single device and ensure consistent policies (like web and content filtering) are enforced, even when users are off network.